When roughly seven hundred supermarkets across France watched their refrigeration units quietly heat up to fifty degrees in the dead of night, nobody expected the grocery aisle to become a geopolitical battleground. Tons of fresh food spoiled overnight, millions of euros vanished in property damage, and Europe woke up to a chilling reality. The digital threat landscape had shifted from corporate data theft to the physical sabotage of everyday life.
Months later, the official investigation reached a breaking point when the French government pointed the finger at Iran, specifically naming the Islamic Revolutionary Guard Corps and an offensive cyber unit known as Shahid Kaveh. Paris didn't just issue a diplomatic warning; the parquet de Paris pushed for international arrest warrants, exposing a brazen state-backed operation that targeted the backbone of the European food supply chain. But beneath the diplomatic fallout lies an uncomfortable truth that cybersecurity experts have warned about for years. Industrial control systems are dangerously exposed, and attackers don't need sophisticated artificial intelligence to cause chaos when basic security hygiene is treated as an afterthought.
The Anatomy of a Cold Chain Sabotage
To understand how a hacker group managed to ruin massive stocks of perishable goods, you have to look at how modern grocery logistics actually operate. Supermarkets rely on automated refrigeration controllers—specifically units produced by Danfoss—to manage temperatures dynamically across hundreds of remote locations.
Convenience often trumps security in industrial engineering. Many of these controllers ran web servers directly accessible over the public internet. Worse yet, a staggering number of installations used default administrative credentials such as "admin" for the username and the current date as the password. Hackers didn't need zero-day exploits or complex quantum algorithms to breach these systems. They just knocked on doors that were left wide open.
Once inside, the attackers altered temperature settings remotely. Refrigerators transformed into heaters. By the time store managers arrived in the morning, dairy, meat, and produce were completely ruined. This wasn't sophisticated espionage aimed at stealing state secrets. It was a blunt instrument designed to inflict maximum economic friction and social disruption.
Why France Pointed Directly at Tehran
Attribution in cyberspace is notoriously difficult. Hackers routinely hide behind proxy groups, false-flag IP addresses, and digital smoke screens. Yet French authorities, backed by independent threat intelligence assessments from corporate giants like Microsoft, felt confident enough to name Tehran publicly.
Several clues tied the operation to Iranian state actors. Investigators found traces of Farsi in digital artifacts left behind on compromised networks. The IP addresses and attack infrastructure matched tools previously linked to Iranian military-affiliated hacking units. Furthermore, front groups claiming responsibility under names like CyberAveng3rs and Cyber Isnaad Front acted as digital megaphones, shouting political slogans while the actual damage was executed behind the scenes.
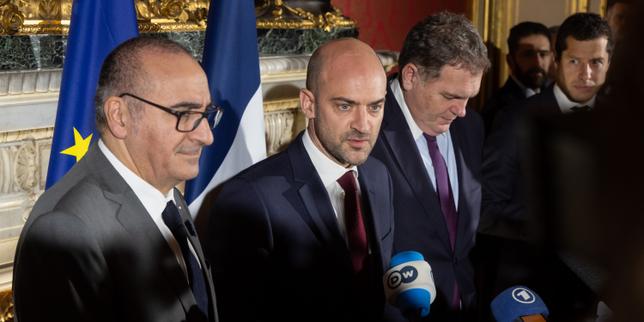
French Foreign Minister Jean-Noël Barrot didn't mince words, calling the incident an unprecedented act of sabotage against national security. The French response went beyond harsh rhetoric. Diplomatic channels buzzed with summons for the Iranian ambassador, and Paris began mobilizing European Union partners to draft harsher economic sanctions. When food safety and basic infrastructure become weapons in a shadow war, standard diplomatic niceties get thrown out the window.
A Broader Pattern of Asymmetric Pressure
The French supermarket incident was not an isolated event. It fit neatly into a wider campaign of pressure hitting Western interests across multiple fronts. Earlier in the year, industrial freezers in Israel experienced similar mysterious malfunctions. Across the Atlantic, military base commissaries operated by the Defense Commissary Agency in the United States suffered unexplained temperature spikes that spoiled food supplies, prompting American defense investigators to eye Tehran with deep suspicion.
Europe has increasingly found itself on the front lines of asymmetric geopolitical friction. Intelligence reports highlight a surge in disruptive activities across the continent, ranging from attempted attacks on military installations to coordinated digital disinformation campaigns designed to amplify social unrest. When direct military confrontation carries too high a cost, state actors increasingly turn to grey-zone tactics. Hacking grocery store cooling units delivers a psychological punch. It reminds ordinary citizens that their daily necessities remain vulnerable to distant conflicts they watch on the evening news.
The Cybersecurity Wake Up Call for Retail
The grocery sector has traditionally viewed itself as safe from high-stakes cyber warfare. Retailers focus heavily on point-of-sale security, customer database protection, and e-commerce platform reliability. Refrigeration units and warehouse climate controls were treated as operational technology rather than digital attack surfaces.
That mindset is completely obsolete. When third-party vendors install connected equipment without enforcing strict multi-factor authentication or closing public-facing administrative ports, they hand attackers a master key to physical infrastructure. Major European retailers faced massive potential losses, proving that physical asset vulnerability carries a staggering financial price tag.
Securing the cold chain requires a complete overhaul of how retail organizations manage operational technology. Businesses must inventory every connected device, eliminate default passwords immediately, and isolate industrial control networks from corporate enterprise IT environments. Relying on perimeter security is no longer enough when an internet-connected thermostat can become a weapon of mass disruption.
Moving Forward in an Era of Fragile Infrastructure
The day France publicly denounced Iran over a batch of ruined grocery store freezers marked a permanent turning point in international cyber relations. It proved that state-sponsored digital attacks can reach directly into the kitchen of an ordinary citizen.
Governments are learning that deterrence in the digital age requires swift, public attribution and coordinated economic retaliation. Meanwhile, private enterprises must stop treating hardware security as an optional checklist item. If we leave our physical infrastructure connected to the public web with default credentials, we invite catastrophe. The next wave of conflict won't just happen on digital screens; it will happen wherever convenience overrides caution.